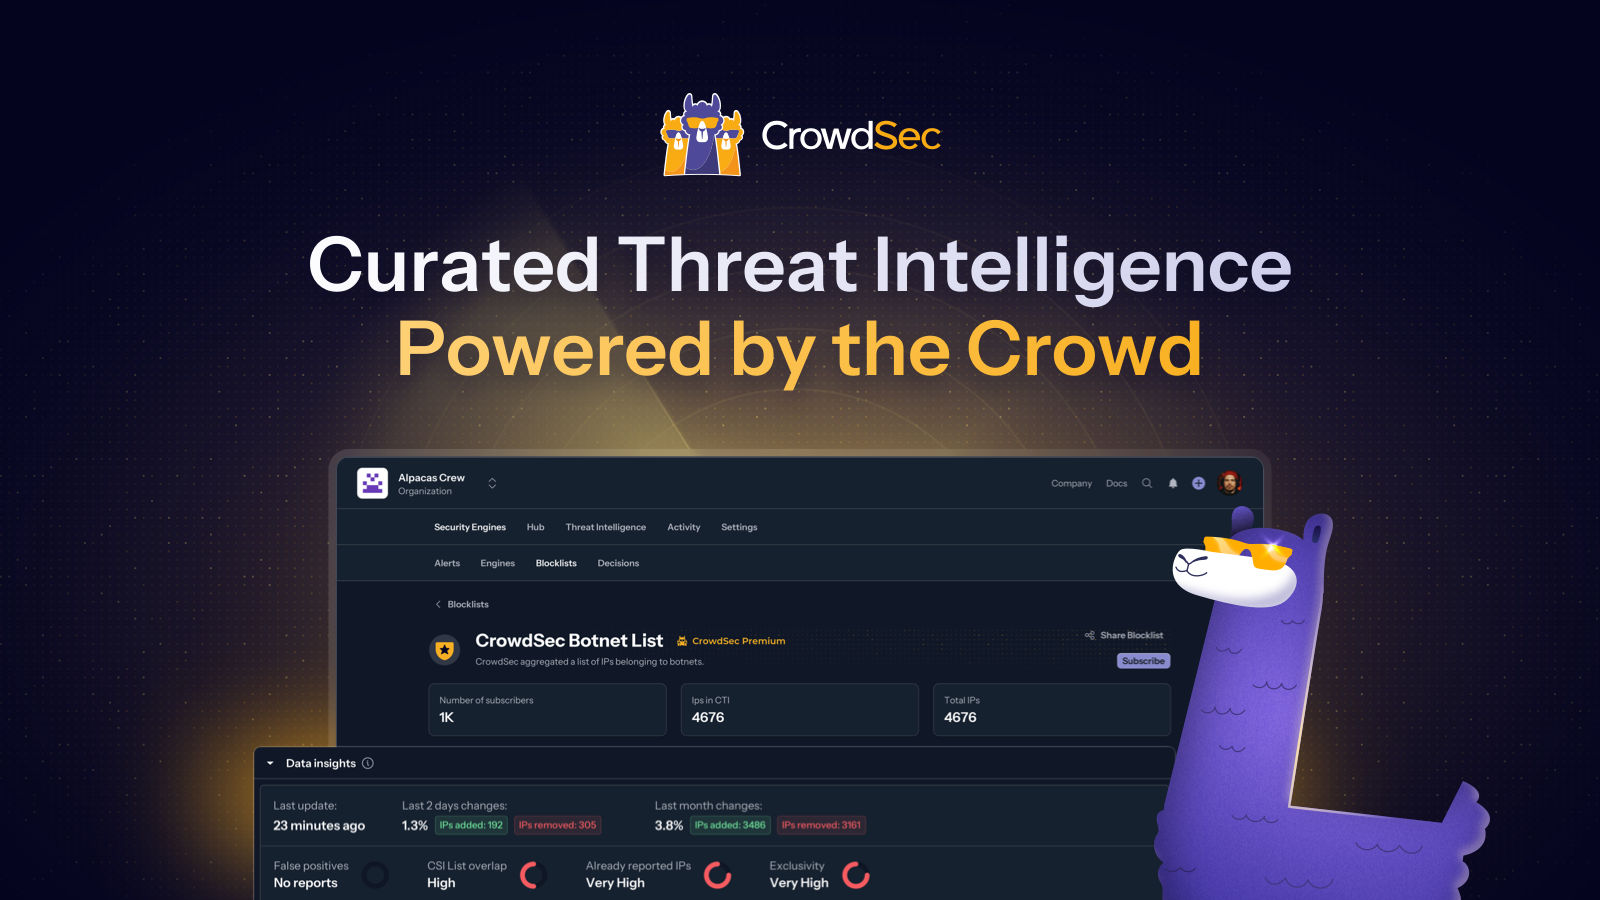

Quick Overview
| Company | CrowdSec SAS (RCS 880 140 496) |
|---|---|
| Category | endpoint protection |
| Headquarters | Montrouge, France |
| Founded | 2020 |
| EU Presence | EU (France) |
| Data Location | European Union |
| Open Source | Yes |
| Compliance | Open source (MIT) |
| Pricing | Free and open source / paid plans for the threat feed |
| Free Option | Free |
| Replaces | Cloudflare bot management, Fail2ban at scale |
Detailed Review
CrowdSec SAS in Montrouge is the odd one in this category and belongs here anyway.
It is open source under MIT, it runs on servers rather than laptops, and it works by reading your logs, spotting attack behaviour, and blocking the addresses behind it — then sharing that signal with everyone else running CrowdSec, so an address hammering a server in Poland is blocked in Portugal before it arrives. Think of it as Fail2ban with a community behind it and a modern architecture.
It does not scan files, it does not protect laptops, and comparing it with ESET on malware detection is comparing two different jobs. What it does do is remove a whole class of noise from internet-facing infrastructure for nothing, with paid plans only for the enriched threat feed and enterprise features. The catch is the usual open-source one: you run it, you configure the scenarios, and the quality of what you get out depends on the attention you put in.
What CrowdSec does well
- Free and open source under MIT, with paid tiers only for the enriched feed
- Community threat intelligence: one attacker blocked everywhere at once
- Built for servers and internet-facing services
- French company, EU processing
Where CrowdSec falls short
- Not endpoint anti-malware; it does not protect laptops
- You run and tune it yourself
- Young company compared with the rest of this list
Standout feature. The network effect turned defensive: every participant blocking an attacker makes the block faster for everyone else.
Pros and Cons
Pros
- Free and open source under MIT, with paid tiers only for the enriched feed
- Community threat intelligence: one attacker blocked everywhere at once
- Built for servers and internet-facing services
- French company, EU processing
Cons
- Not endpoint anti-malware; it does not protect laptops
- You run and tune it yourself
- Young company compared with the rest of this list
Alternatives to CrowdSec
Frequently Asked Questions
What is CrowdSec?
CrowdSec SAS in Montrouge is the odd one in this category and belongs here anyway.
It is open source under MIT, it runs on servers rather than laptops, and it works by reading your logs, spotting attack behaviour, and blocking the addresses behind it — then sharing that signal with everyone else running CrowdSec, so an address hammering a server in Poland is blocked in Portugal before it arrives. Think of it as Fail2ban with a community behind it and a modern architecture.
Where is CrowdSec based?
CrowdSec operates from Montrouge, France, which places it under EU (France). Compliance: Open source (MIT).
What does CrowdSec cost?
Free and open source / paid plans for the threat feed. Free.
Who is CrowdSec best for?
Teams protecting internet-facing servers who want shared threat intelligence without a licence. The network effect turned defensive: every participant blocking an attacker makes the block faster for everyone else.
What are the drawbacks of CrowdSec?
Not endpoint anti-malware; it does not protect laptops. You run and tune it yourself. Young company compared with the rest of this list.
Is CrowdSec a good alternative to Cloudflare bot management?
CrowdSec is built as a European alternative to Cloudflare bot management: Open-source server protection with shared threat signals. It will not be a like-for-like feature match in every respect, so check the review above for where the two genuinely differ before switching.
How does CrowdSec compare to other endpoint protection tools?
CrowdSec is one of several European endpoint protection tools we cover. It is most often compared with Cloudflare bot management, Fail2ban at scale.